DNS MX record

We just started to chat about DNS records with the DNS A Records, and now we will see a second DNS record – DNS MX record. MX does not mean Mexican. It means Mail Exchanger. We will go into details about why such a DNS record must exist and why can’t we freely send emails the way we want. 

Check this page if you need additional information about the DNS MX record!

What is a DNS MX record?

Every action that relates to domains needs DNS records for instruction. In the DNS MX record case, it is a text document, mail exchanger record, that shows which server is responsible for receiving the emails that go for a particular domain. 

(more…)

DNSSEC

The Domain Name System is one of the Internet’s essential services. It translates familiar domain names into the IP addresses that computers use to communicate. That convenience also creates an important security question: how can a resolver know that the DNS answer it received is authentic and has not been replaced in transit?

DNS Security Extensions, usually called DNSSEC, address that problem with digital signatures. DNSSEC allows a validating resolver to verify where DNS data came from and whether it changed after the authoritative zone signed it. It strengthens trust in DNS without replacing the DNS protocol or encrypting ordinary DNS queries.

What problem does DNSSEC solve?

Traditional DNS was designed for availability and speed, not for cryptographic verification. A resolver can ask an authoritative server for a record, but the basic protocol does not prove that the response is genuine. An attacker who succeeds in inserting a forged answer could direct visitors to an unintended server even when they typed the correct domain name.

This risk is easier to understand after reviewing how the Domain Name System resolves a name. DNSSEC adds verifiable signatures to that process. A validating resolver can reject a forged or altered response instead of treating it as legitimate DNS data.

How DNSSEC creates a chain of trust

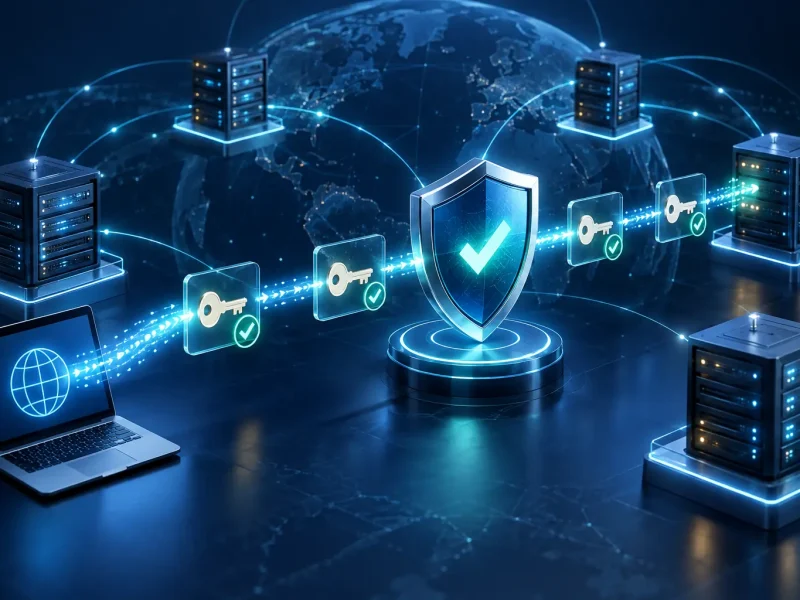
DNSSEC does not rely on one universal key for every domain. It creates a chain of trust that begins at the DNS root and continues through the top-level domain to the signed domain. Each level can securely point to the key used by the level below it.

DNSKEY records publish public keys

A signed zone publishes its public keys in DNSKEY records. The corresponding private keys remain protected by the zone operator and are used to sign groups of DNS records. Keeping the private key secure is critical because anyone who obtains it may be able to produce signatures that appear valid.

RRSIG records contain digital signatures

For each signed record set, the authoritative zone supplies an RRSIG record. A validating resolver uses the appropriate DNSKEY to check that signature. Successful validation confirms both the origin of the data and its integrity: the response was signed by the expected zone and was not modified after signing.

DS records connect parent and child zones

A DS record in the parent zone contains a digest associated with a key in the child zone. For example, a registrar can publish a domain’s DS information in the relevant top-level-domain zone. The resolver follows these references from a previously trusted level, building a verifiable path to the final answer.

NSEC and NSEC3 authenticate negative answers

DNSSEC must also prove when a requested name or record does not exist. NSEC and NSEC3 records provide authenticated denial of existence. This prevents an attacker from simply returning an unsigned “not found” response for valid signed data.

What DNSSEC protects—and what it does not

DNSSEC provides DNS data origin authentication, integrity protection, and authenticated denial of existence. These controls help defend against forged DNS answers and cache-poisoning scenarios when validation is performed correctly.

However, DNSSEC does not encrypt DNS traffic. Anyone able to observe an unencrypted DNS query may still see the requested name. DNSSEC also does not secure a vulnerable website, repair an infected server, prevent every distributed denial-of-service attack, or protect a registrar account with a weak password. HTTPS, access controls, monitoring, backups, and secure account practices remain necessary.

Why deployment has two important sides

DNSSEC works only when zone signing and validation connect correctly.

  • Authoritative side: The domain owner or DNS provider signs the zone, publishes DNSKEY and signature records, and keeps the signatures current.
  • Parent-side delegation: The correct DS record is published through the registrar or registry so the parent can establish trust in the child zone.
  • Resolver side: A validating recursive resolver checks the signatures and the chain of trust before returning an answer to the client.

If a signed zone changes its keys without updating the parent DS information correctly, validating users may receive failures even though the records look normal to a non-validating resolver. Careful key rollover and monitoring are therefore part of operating DNSSEC, not optional housekeeping.

A practical DNSSEC deployment checklist

  1. Confirm support. Check that the authoritative DNS provider, registrar, and top-level domain all support the required DNSSEC workflow.
  2. Review current DNS data. Make sure the zone is accurate before signing it. DNSSEC can authenticate incorrect data just as effectively as correct data.
  3. Enable zone signing. Generate or activate the signing keys through the authoritative DNS service and confirm that DNSKEY and RRSIG records appear.
  4. Publish the DS record. Submit the exact DS values through the registrar. A mismatch can break validation for the domain.
  5. Test from validating resolvers. Confirm the complete chain of trust, not merely the presence of DNSSEC records.
  6. Monitor signatures and rollovers. Watch expiration dates, DS consistency, and planned key changes. Include DNSSEC checks in routine DNS monitoring.

Reliable authoritative infrastructure still matters after a zone is signed. Features such as redundant servers, anycast distribution, monitoring, and failover address availability rather than authenticity. The distinction is similar to the operational benefits discussed in the guide to Premium DNS: security and resilience are strongest when several complementary controls work together.

DNSSEC is a trust layer, not a complete security stack

A successful DNSSEC deployment gives validating resolvers cryptographic evidence that DNS data is authentic. It reduces an important class of DNS manipulation risk, but it should be combined with HTTPS, secure registrar access, multi-factor authentication, protected signing keys, monitored DNS changes, and resilient authoritative service.

For a practical overview of the technology, see DNSSEC, the DNS Security extension. The protocol’s security model and requirements are defined in RFC 4033: DNS Security Introduction and Requirements.
Premium DNS

Premium DNS explanation

You may get more of everything with a Premium DNS service. More DNS zones and DNS servers are available. You can also better control the flow of traffic. You’ll notice a difference in loading speed once you start utilizing it. It will also result in improved uptime, security, and SEO.

If downtime is not an option for your company, the Premium DNS service should be explored. Implementing a DNS service like this could benefit any website larger than a small personal blog.

If visitors continue to rise, you should seriously consider using this service.

(more…)

Free DNS service

Free DNS service explained in details

Free DNS service gives your domain name the ability to be visible on the Internet. It provides simple and basic DNS infrastructure, allowing users to access your website.

This service is excellent for you if you manage a blog or a small local online business. Free DNS service delivers a stable domain, some features for DNS (Domain Name System) management, and average speed. It is an absolutely free opportunity. 

(more…)

IPv4 IPv6

IPv4 and IPv6 are two different versions of Internet protocol (IP). For that reason, it is important to understand what are the differences between them. So, let’s explain a little bit more!

Internet Protocol (IP) – What is it?

Internet protocol, or as we know it, more popular as IP, establishes a group of communication rules which control the format of the information transferred among the networks or the Internet. 

Thanks to the IP, it is easy to set the most suitable structures for packets to transport data until they are delivered. In addition, it includes several methods for addressing, and it routes datagrams across networks. Therefore, the transportation of data packets from their origin to their target destination depends on IP addresses.

When it comes to connections on the Internet, it is crucial to know who is requesting some data and who is supposed to provide the information, like routers, websites, servers, Internet of Things, and so on. IP addresses serve for identifying and connecting with the machines, devices, servers. That makes it possible to achieve communication and exchange of information.

(more…)

Domain parking

What is domain parking?

Domain parking is a service (usually free) that domain registrars offer to their clients (people who got themselves a domain name) to have a simple, non-interactive, single HTML page, where the clients can put their contact information and a short text message with more details about the future of the domain name.

(more…)

TXT record

Domain Name System (DNS) includes many different records to execute different functions required for the Internet to work as easily and efficiently as users expect.

TXT records’ functionality is absolutely essential. Check out why to use TXT record.

What is the TXT record?

Text or TXT record is a DNS record that holds text information related to a domain for external sources to read it. TXT records commonly have general information about a domain and important data frequently used for validating (security processes). They can validate information for e-mailing or for confirming if you really are the owner of a domain.

When created, the TXT record was for administrators’ notes. But machines have evolved through the years, and such text notes are also legible for them. This is very convenient for administrators because using TXT records, they can send text entries into the DNS, with specific instructions for machines to accomplish.

Do you know how to prevent your emails from going to spam? Check how DNS TXT record can help you!

(more…)

IaaS

In the last years, cloud computing services have become very popular. But still, while chatting with colleagues, some confusion comes around the term and the kinds of services that it involves.

What is cloud computing?

Shortly, cloud computing is an on-demand supply of tech resources through the Internet in exchange for a defined fee. Rephrasing, you can get everything you need, from data centers, servers, storage, databases, networking, software, etc., without the need to own them directly.

(more…)

DNS A record

Understanding DNS record is easy. The only thing that you need a simple explanation. We will see what a DNS record is, and we will start speaking about one of the most used ones – DNS A record. It is the simple record that connects what you are typing in your web browser and the address of the site, but let’ go in-depth. 

In the following page you can find in-depth information about the A record!

DNS and DNS records explained

We will not go into detail, but we should really define what DNS and DNS records are before we go to the topic of DNS A records. 

(more…)

Domain Name System

The time before the Domain Name System

A long, long time ago, there was no Internet! Can you believe it? Back then, there were just a few university computers and some military ones linked together through different networks. They were working together, but with a lot of connection problems. The number of the devices started to grow, so did the connection between them. 

Back then, each of the computers needed to have a hosts.txt file on their memory, which was basically a table with hosts’ names and their IP addresses. Like a table of A records, but of all possible devices that are there. 

Imagine having to administrate a massive excel table with all the sites that you want to visit and their addresses. A lot of work! 

The hosts.txt was not a viable option, so there was a need for a better system for that new thing called the World Wide Web. This is where the Domain Name System came. 

Domain Name System explained

(more…)

DHCP

To keep running a network demands dividing administrators’ attention and time among many tasks. All are necessary. Some are really exciting. And others… Well, no job is perfect. Others can be really boring, and besides, they can require a lot of time.

Fortunately, technology is focused not only on developing new and amazing stuff but also on making daily and boring tasks easier, sometimes automatic. And that is the case of DHCP. 

What is DHCP?

Dynamic Host Configuration Protocol (DHCP) is a management protocol very used on networks (TCP/IP) through its installation on servers. It is a tool for assigning IP addresses and more needed data automatically. Networks and connected devices to communicate need default gateways, subnet masks, and other configurations. 

Advantages and Disadvantages of DHCP

(more…)

Load More